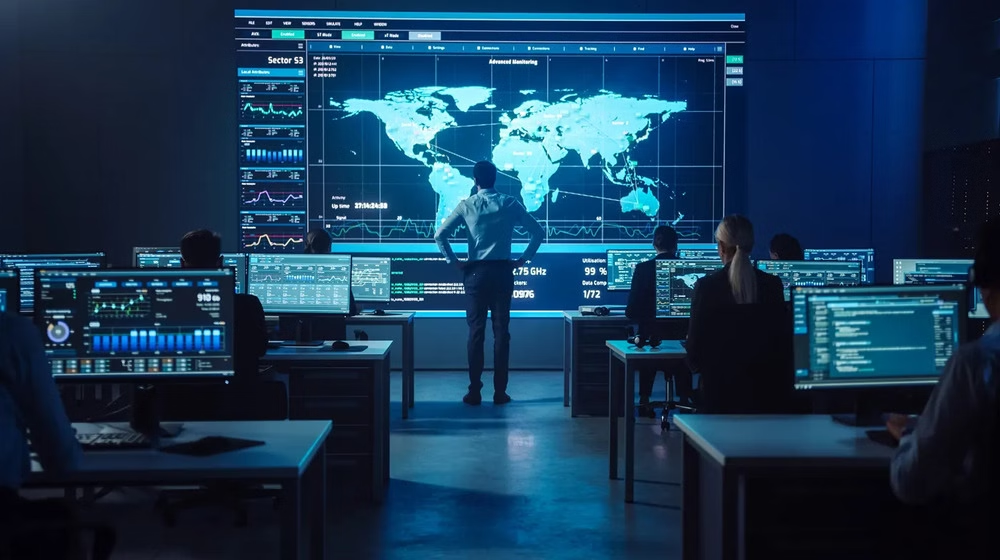
The Pakistan Threat Intelligence System has been officially operationalized to unify the nation’s cyber defenses and safeguard critical infrastructure from sophisticated state-sponsored attacks. Developed by the National CERT, this centralized platform integrates the Pakistan Army Cyber Division-101 and the Pakistan Telecommunication Authority (PTA) into a single, coordinated shield against digital threats.
Follow us for More:
Strengthening Sovereignty via the Pakistan Threat Intelligence System
This development marks a decisive shift toward “cyber sovereignty” by reducing Pakistan’s reliance on foreign intelligence feeds. By utilizing the Malware Information Sharing Platform (MISP), the system enables the government to govern its own data while identifying Indicators of Compromise (IoCs)—such as malicious IP addresses and attack hashes—in real time.
Key Capabilities of the New Framework
According to official sources, the integration focuses on high-stakes sectors including power grids, banking networks, and telecom systems. Key features include:
- Real-Time Correlation: Centralized data analysis to detect early-stage “Advanced Persistent Threats” (APTs).
- Predictive Defense: Transitioning from reactive patching to proactive “threat hunting.”
- Joint Response: Seamless escalation and communication between military and civilian authorities during active breaches.
Combatting Supply Chain Vulnerabilities
The launch of the Pakistan Threat Intelligence System follows a high-priority advisory from the National CERT warning of “hostile actors” targeting national supply chains. Officials noted that by sharing real-time intelligence, the impact of a breach in one sector can be contained before it paralyzes the entire national grid.
Through this unified posture, Pakistan aims to secure its national interests in cyberspace and provide a robust response to the evolving regional security landscape. For more information on cybersecurity compliance, visit the Pakistan Telecommunication Authority (PTA).